 Sistematiko
Artificial intelligence
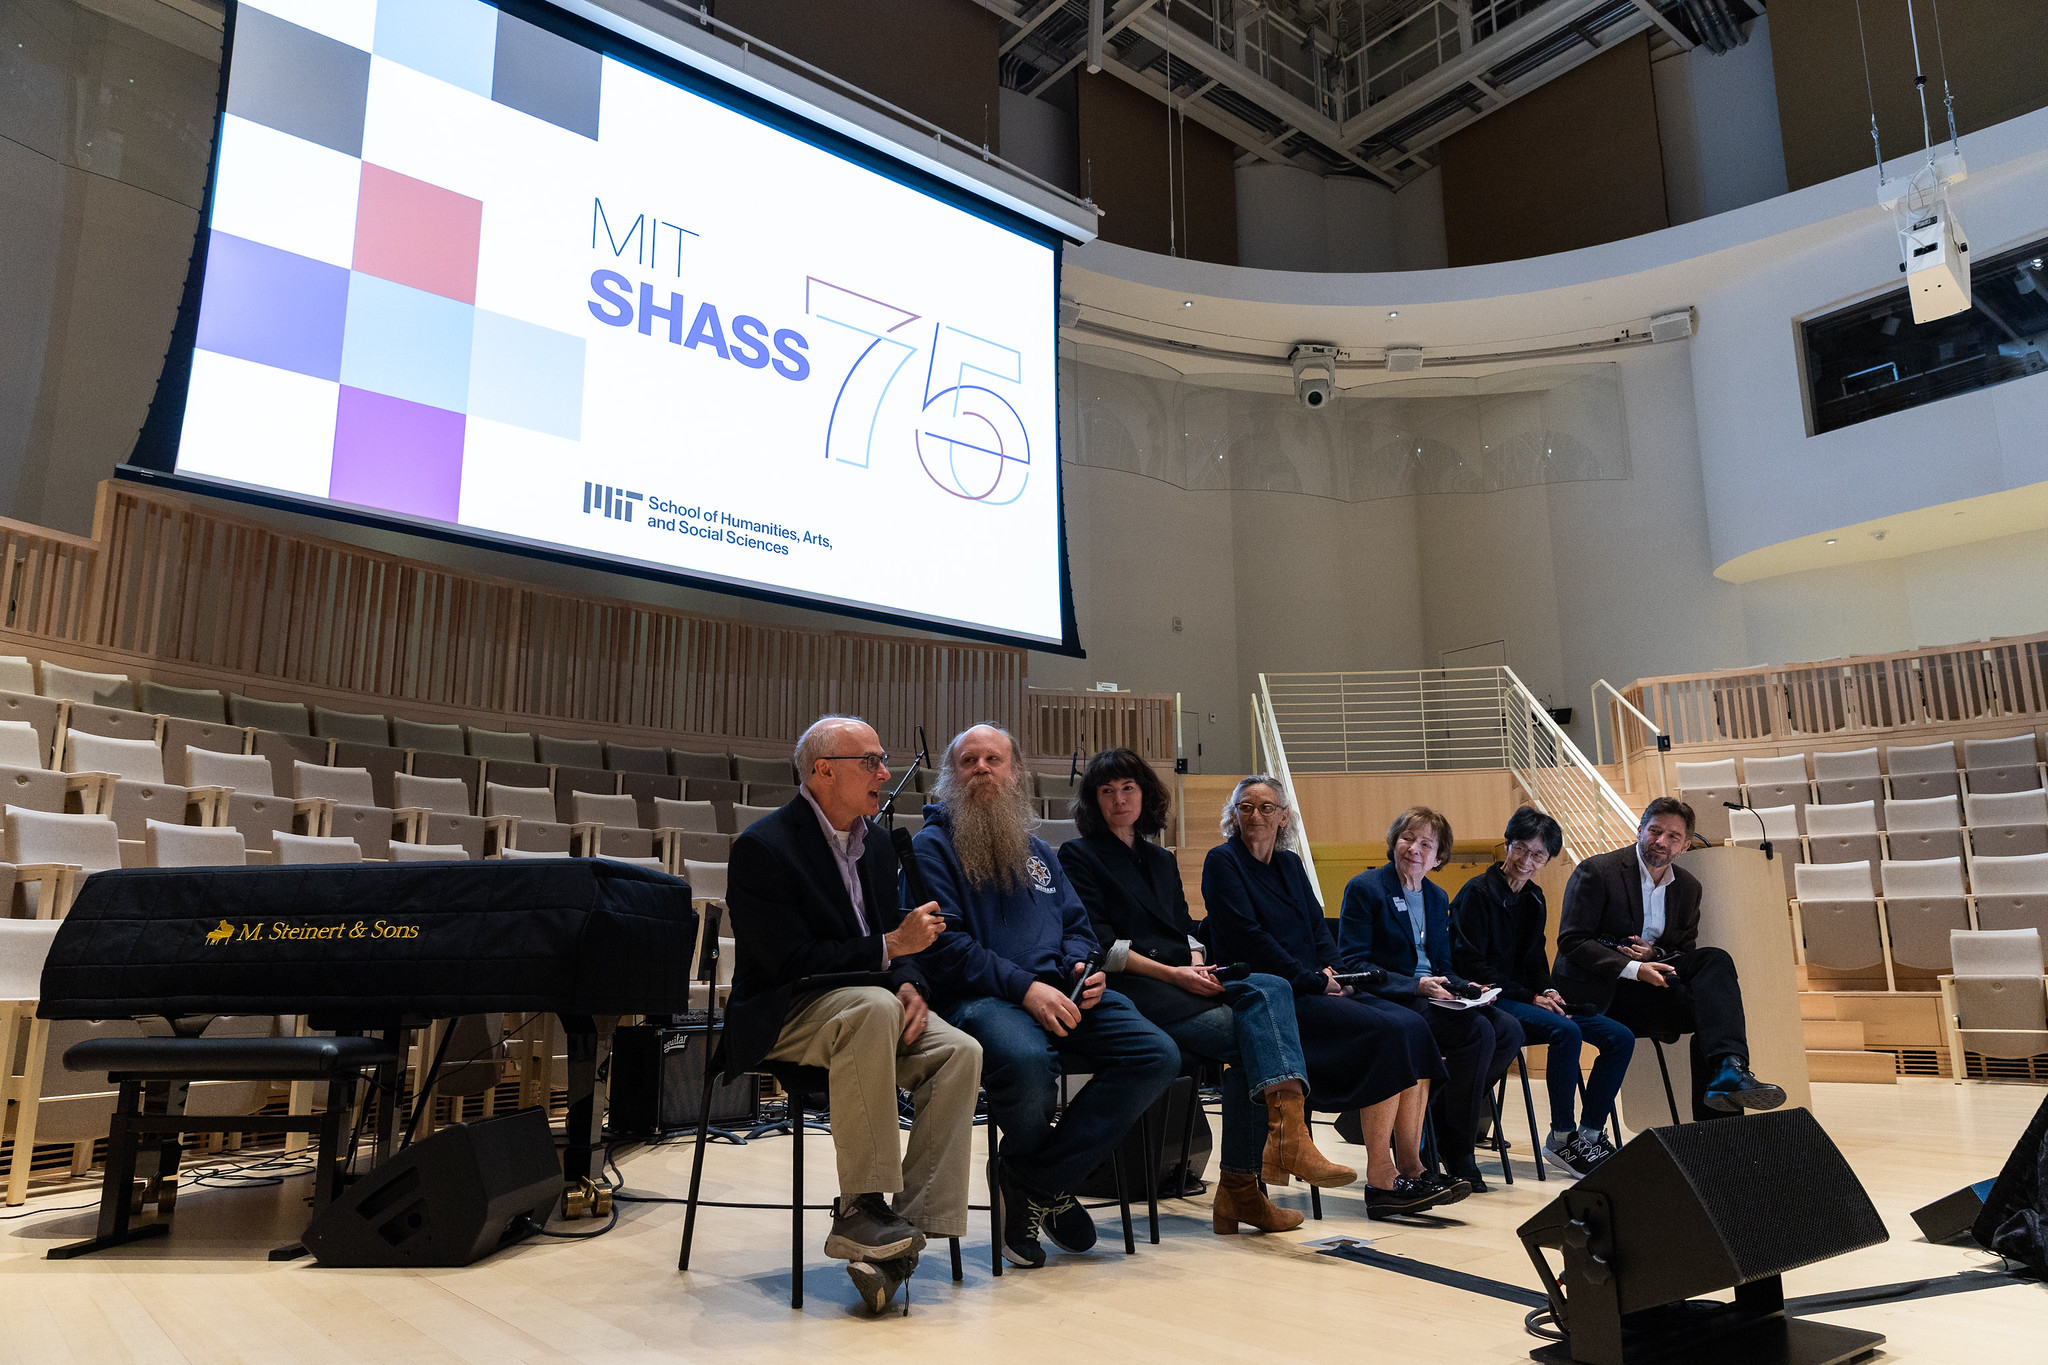
Reinforcing the value of human understanding at MIT
MIT News — Artificial Intelligence · Oct 24, 2026
Recent programming, artificial intelligence, computer science, operating-system, web-development, and cybersecurity stories collected from established publishers. Headlines open on the original publisher’s website.
Feed updated Oct 24, 2026 · 4:55 AM PHT
The latest image-supported stories across every category.
MIT News — Artificial Intelligence · Oct 24, 2026
MIT News — Artificial Intelligence · Oct 23, 2026
MIT News — Artificial Intelligence · Oct 23, 2026
MIT News — Artificial Intelligence · Oct 20, 2026
MIT News — Artificial Intelligence · Oct 18, 2026
Researchers remotely disabled a vulnerable updater in the abandoned Time4Popcorn app, a fork of the Popcorn Time BitTorrent client, closing a security flaw that could have allowed attackers to execute malicious code with elevated privileges on millions of com…
BleepingComputer (opens in a new tab)Microsoft has announced plans to add AI-powered phishing detection to Teams messages starting in early November 2026. [...]
BleepingComputer (opens in a new tab)Diplomatic organizations in Central Asia have been targeted by a sophisticated new Unified Extensible Firmware Interface (UEFI) bootkit called BlackX. The activity, which singled out diplomatic entities in Tajikistan, Uzbekistan, and Turkmenistan in early 202…
The Hacker News (opens in a new tab)Ruby has released versions 4.0.9, 3.4.12, and 3.3.13 to fix three bugs in Onigmo, the regular expression engine built into the language. The bugs lie behind four critical security flaws that GitLab patched over the past month. GitLab found that a specially cr…
The Hacker News (opens in a new tab)Cybersecurity researchers have discovered an artificial intelligence (AI)-driven intrusion ecosystem run by affiliates of the INC and The Gentlemen ransomware groups. Central to the operation is an "Autonomous Red Team Kill Chain Framework" referred to as Pha…
The Hacker News (opens in a new tab)Microsoft says Windows Server 2016 will stop receiving security updates after it reaches the end of support in January 2027. [...]
BleepingComputer (opens in a new tab)American clinical laboratory company Quest Diagnostics disclosed that patient records have been exposed after a threat actor gained unauthorized access to its Quanum LSM system. [...]
BleepingComputer (opens in a new tab)The PHP security team has shared mitigation measures for a new remote code execution vulnerability that affects systems with non-default configurations and has no patch. [...]
BleepingComputer (opens in a new tab)AI agents can be manipulated through malicious emails, websites, and plugins into executing commands, stealing data, or deleting files using their legitimate permissions. Gen Digital explains how its Agent Trust Hub helps protect agents through skill verifica…
BleepingComputer (opens in a new tab)Cybersecurity researchers have disclosed details of a large-scale campaign that has targeted exposed network edge devices such as Fortinet FortiGate and Palo Alto Networks GlobalProtect firewalls. "Artifacts from this investigation also indicate that operator…
The Hacker News (opens in a new tab)Hewlett Packard Enterprise (HPE) released security updates to patch 72 vulnerabilities in the Aruba Operating System (ArubaOS), including eight maximum-severity authentication bypass and code execution issues. [...]
BleepingComputer (opens in a new tab)PHP has warned of another way an attacker could run code on a web server, two days after it shipped emergency fixes for the critical PHP2Shell flaws. The new issue, assigned CVE-2026-115560, affects only web applications configured in an unusual way, and PHP …
The Hacker News (opens in a new tab)The Russian state-sponsored hacking group Sandworm teamed up with another threat actor to carry out a destructive wiping attack targeting a Ukrainian logistics company last year. According to ESET, the attack involved UAC-0099 (aka Earth Sirrush) obtaining in…
The Hacker News (opens in a new tab)Pillow, the most widely used image library for Python, can be made to run operating system commands on a server by specifying the name of a file it is told to open. The flaw, CVE-2026-112900, is in the way Pillow handles EPS images, which it opens by pas…
The Hacker News (opens in a new tab)Malicious Brotli data can make an application on an official build of Node.js run attacker-supplied code, security researchers at Imperva have demonstrated. Their "Node2Shell" proof of concept ran code on the official Node.js 24.22.0 image for Linux arm6…
The Hacker News (opens in a new tab)AI agents paying for API calls with the x402 SDKs could sign a payment for their full balance of a supported token if a malicious API asked for it, security firm V12 said on October 22. The cause was the SDKs' default client, which set no …
The Hacker News (opens in a new tab)Threat actors have been observed unsuccessfully attempting to exploit the newly disclosed PHP2Shell vulnerabilities to rope infected systems into a Mirai botnet variant called Potassium, as it emerges that weaponizing the flaws may be harder than previously t…
The Hacker News (opens in a new tab)Cloud platform Railway published an urgent warning to users after detecting suspicious activity on its systems that store customer environment variables earlier this week. [...]
BleepingComputer (opens in a new tab)Japanese gaming giant Capcom has confirmed that hackers breached its membership service, CAPCOM ID, exposing more than 11.7 million customer email addresses and associated information. [...]
BleepingComputer (opens in a new tab)Hackers compromised the LiteLLM project's PyPI package and published malicious Docker images with a payload that steals credentials, secrets, and environment variables. [...]
BleepingComputer (opens in a new tab)